Travel businesses are being warned that their biggest cyber security risk is not their technology but their people, after two industry events heard that AI has made hacking ‘child’s play’ and that travel staff overshare more than almost any other sector.
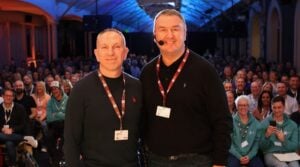
Hackers no longer need to be skilled to break into a business, and a 12-year-old could now do it, delegates at the Leaders in Travel summit, organised by travel accountants Xeinadin, were told.
PC Simon Baker of the Met Police’s Cyber Education Team said AI had turned hacking into child’s play, and he pointed to a ‘huge’ rise in AI-enabled attacks.
“The travel industry gets hit hard all the time,” he said, adding that Report Fraud (formerly Action Fraud) is currently seeing a lot of bogus Booking.com payment links being sent by email.
Even companies with tight security can be exposed through their suppliers, he warned, adding that supply chain attacks have risen 400% in the past four years.
“You might be doing the right things, but someone in your supply chain might not,” he said. One company that lost millions of pounds after fraudsters cloned the faces of people in its supply chain for a Teams call, he added.
Simon said 90% of cyber attacks come down to human error, such as weak passwords or replying to phishing emails and bogus messages on Teams, WhatsApp or email.
Staff should always verify anything suspicious through a separate channel, and should be wary of messages arriving on an unusual platform. “If Janet messages you on LinkedIn and that isn’t normal for her, find another way to contact her to verify the message is real,” he said.
Homeworkers are particularly vulnerable because they are more easily distracted. “They might be taking a work call one minute and washing the dishes the next,” he said.
His advice was to use VPNs on all devices, including for homeworkers, and to force software updates. “Don’t give staff the option; make sure computers update overnight,” he said. He also urged firms to issue company phones and laptops, adding: “I would not let people use their own devices.” Public wifi, such as at airports, should be avoided, or used only with a VPN, he said.
Every business also needs an ‘instant rescue plan’ that key staff know about and can find, and that is tested and improved regularly. “If you’ve given it to John and he is in the Maldives for a week, what are you going to do?” asked Simon.
A cyber attack can cause a ‘humongous’ amount of reputational damage, he warned. “We need to train ourselves, we need to train our colleagues, and we need to pass that knowledge on to our clients.”
One delegate told the session that their company’s bank details had been stolen and changed after an internal email containing an invoice was intercepted, and said reporting it had been difficult. “I felt we were too small and insignificant.”
‘I can’t think of another industry that overshares as much as yours’
The same message came through at the ABTA Travel Convention, where a session called Burglar for Hire heard that it is far easier to break into a business through its staff than by physically breaking in.
Social engineer Jenny Radcliffe, author of People Hacker, is hired by companies to test whether she can get past their security by conning their staff.
She told delegates that travel was particularly exposed. “We have this whole problem through the industry that you’re telling people a lot of things about you all the time,” she said. “I can’t think of another industry where people are as guilty of oversharing as yours.”
Posting pets’ names, photos of homes, hobbies and favourite charities on social media gives hackers enough detail to write convincing phishing emails and texts, she said. Many data breaches have already exposed names, dates of birth and addresses, so criminals can send messages that show they know a lot about their target. She noted that criminals would have known many in the industry were away at The Savoy Palace in Madeira for the convention.
She singled out WhatsApp as a particular risk because people trust it, and said too many people reuse passwords and believe security is not their problem.
Training should be made human, she said, with people given a free pass to talk about it openly in meetings. Since people already care about not being hacked on their own social media, security should be treated as something everyone cares about, not a specialist topic. The consequences of ignoring it are significant, she warned.
Free cyber security advice is available from local police forces.